


Case studies reais
Networks, Wi-Fi, servers and security systems installed and managed by us — in hotels, clinics, offices and multinational companies operating in Portugal.

Ubiquiti success story: more than 138 sites, many with redundancy and u...
How DataRoad brought Ubiquiti to Portugal and turned it into a reference solution for business networks, with more than 138 sites and 1321 available...
View the case
Forward College — IT network and support at the Lisbon campus
Forward College, a European higher education institution with a campus in Lisbon, has chosen DataRoad as its IT partner for its operations in Portugal. U...
View the case
Magnelusa — Computer network installation
Magnelusa, a leading Portuguese company in its sector, commissioned DataRoad to install the IT network at its premises. It was necessary...
View the case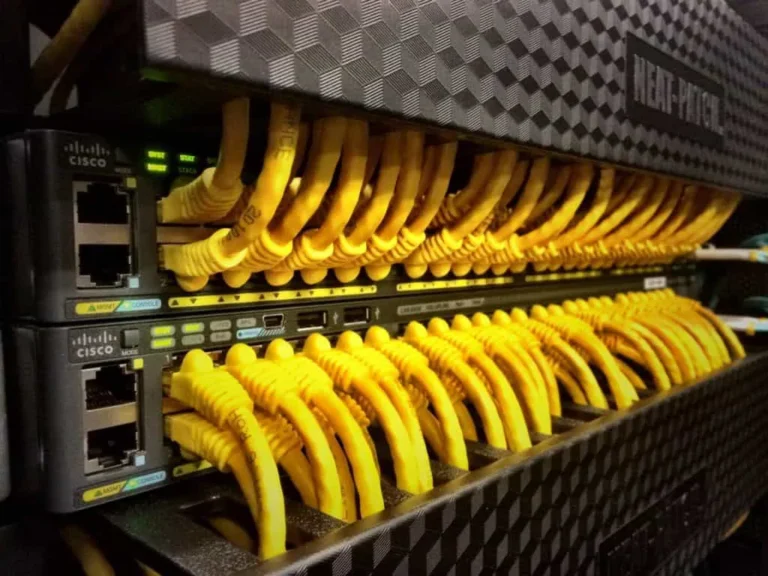
Klass Wagen — IT infrastructure for car hire operations in Portugal
Klass Wagen, a rapidly growing international car hire company in Europe, has entrusted DataRoad with the IT infrastructure for its operations in Portugal....
View the case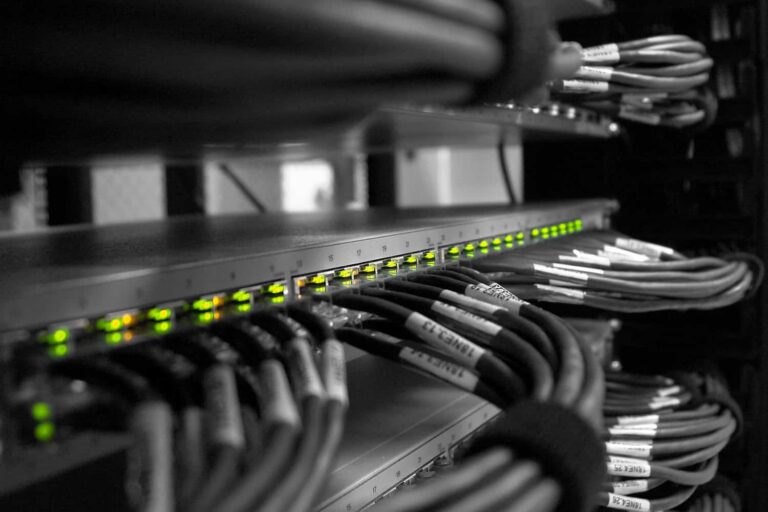
Panike — Network and communications infrastructure in the food industry
Panike, a leading national name in the production of pastries and baked goods, has chosen DataRoad to strengthen the network and communications infrastructure of its...
View the case
Public Sector
SSAP: structured networks and 56 Wi-Fi 7 access points across three buildings
Structured networks and 56 WiFi 7 access points in three buildings belonging to the Public Administration’s Social Services, following a public tender.
View the case
Companies - Multinationals
ReStream — Complete IT network (Wi-Fi 6, firewall, Starlink) in the office...
A fully equipped IT network at ReStream’s office in Cascais: Wi-Fi 6, a firewall and a Starlink connection for redundancy.
View the case
Companies - Multinationals
Reltio by SAP — IT Unlimited’s IT maintenance and consulting services at the office...
IT Unlimited IT maintenance and consulting services at the Lisbon office of Reltio by SAP, with fixed monthly support costs.
View the case
Hospitality
LX Arch Hotel (Rua Augusta, Lisbon) — Full IT set-up, Wi-Fi 7,...
A comprehensive IT installation at the LX Arch Hotel on Rua Augusta: WiFi 7 in all rooms, CCTV and ongoing IT management.
View the case
Clinics and Health
Lambert Clinic (Corroios) — Comprehensive IT support from IT Unlimited, network and Wi-Fi...
Comprehensive IT support, including corporate network and wireless services, at Clínica Lambert in Corroios, under an IT Unlimited contract.
View the case
Clinics and Health
Clínica Mulher (Twin Towers, Sete Rios) — Full IT network, WiFi 7 and...
A fully equipped IT network, Wi-Fi 7 and IT Unlimited support at Clínica Mulher, in the Twin Towers in Sete Rios, Lisbon.
View the case
Hospitality
Ouro Rossio Hotel — Comprehensive IT infrastructure, Wi-Fi and CCTV for guests...
How we fitted out the Ouro Rossio Hotel, in Restauradores, with a complete IT infrastructure: a network, Wi-Fi for guests and CCTV.
View the caseDataRoad projects and success stories
DataRoad blog articles and news
- Boost Portugal: total network renewal, Wi-Fi and firewall
- Reltio by SAP: cabling, firewall, Wi‑Fi, and Dell and Apple workstations
- Mitrelli Group: 3,000 m of cabling, Wi-Fi 6 and video surveillance
- UpHill Health: network, Wi-Fi 6, firewall and biometrics in Lisbon
- ReStream — Full IT network (Wi-Fi 6, firewall, Starlink) at the Cascais office
- Beqom: network, firewall and IT Unlimited for 60 workstations in Lisbon
- Ventask: IT Unlimited for 350 workstations, firewalls and switches
- Velv by OnRising chooses DataRoad: an IT Unlimited contract for 90 workstations, a firewall and a wireless network (2023)
- Backup and disaster recovery: how long can your SME keep going when it’s down?
- FreshDesign: firewall, SSL VPN and internet redundancy
- IP Video Surveillance for Businesses: Design, Networking and Legal Requirements
- Harland & Poston: network, firewall and Wi-Fi on Av. da Liberdade
- Cisco Meraki: MX95 firewall, switches and wireless coverage
- Company Wi-Fi Security: Guests, Passwords and What You Should Never Share
- Klass Wagen: network, Wi-Fi, firewall and video surveillance in Funchal
- Cybersecurity Checklist for SMEs in Portugal
- OnRising: biometric access control and network firewall
- Firewalls for Businesses: What They Do, What They Don’t Do and How to Choose One
Managed cybersecurity for your company
Request an assessment without obligation.
*Call to the national fixed network · Companies with more than 10 locations · Remote, local and telephone support